

How to Choose Trusted Security Service Providers
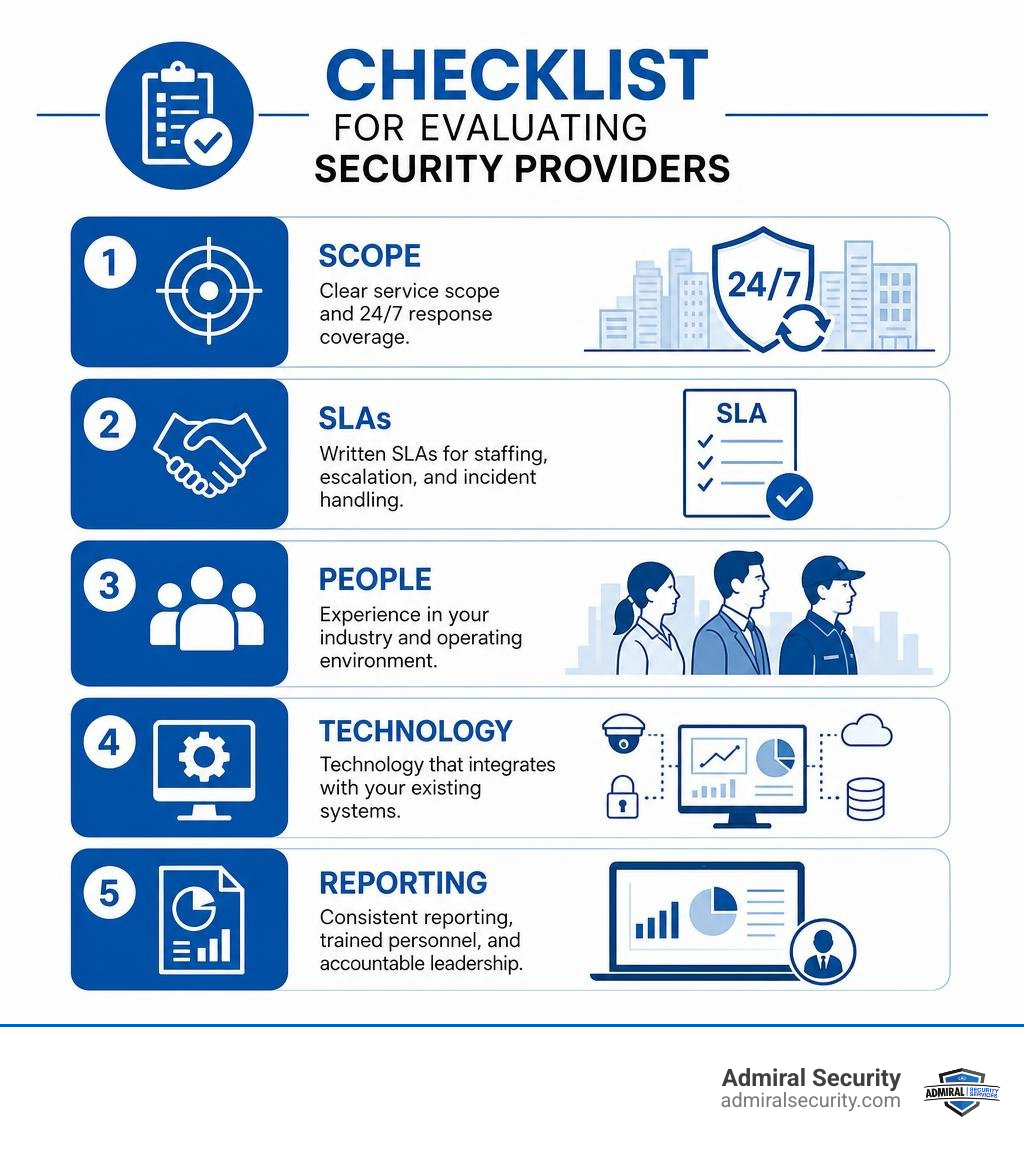
Trusted security service providers match their staffing, technology, response times, and reporting to your real risks. Start by defining what you need most: reliable on-site officers, remote monitoring, cyber threat response, compliance support, or a combined approach. Then compare providers on these essentials:
- Clear service scope and 24/7 response coverage
- Written SLAs for staffing, escalation, and incident handling
- Experience in your industry and operating environment
- Technology that integrates with your existing systems
- Consistent reporting, trained personnel, and accountable leadership
For commercial real estate, retail, and operations teams, the right partner does more than fill shifts or watch alerts. It supports smooth daily operations, represents your brand well, and helps your team respond quickly when issues arise.
The stakes are high. In 2026, the average cost of a data breach reached $4.99 million, while AI-driven attacks increased. At the same time, many organizations manage more than 50 security tools that do not work well together. A dependable provider can simplify that complexity through trained teams, connected monitoring, and clear ownership.
Understanding Modern Security Service Providers and Core Delivery Models
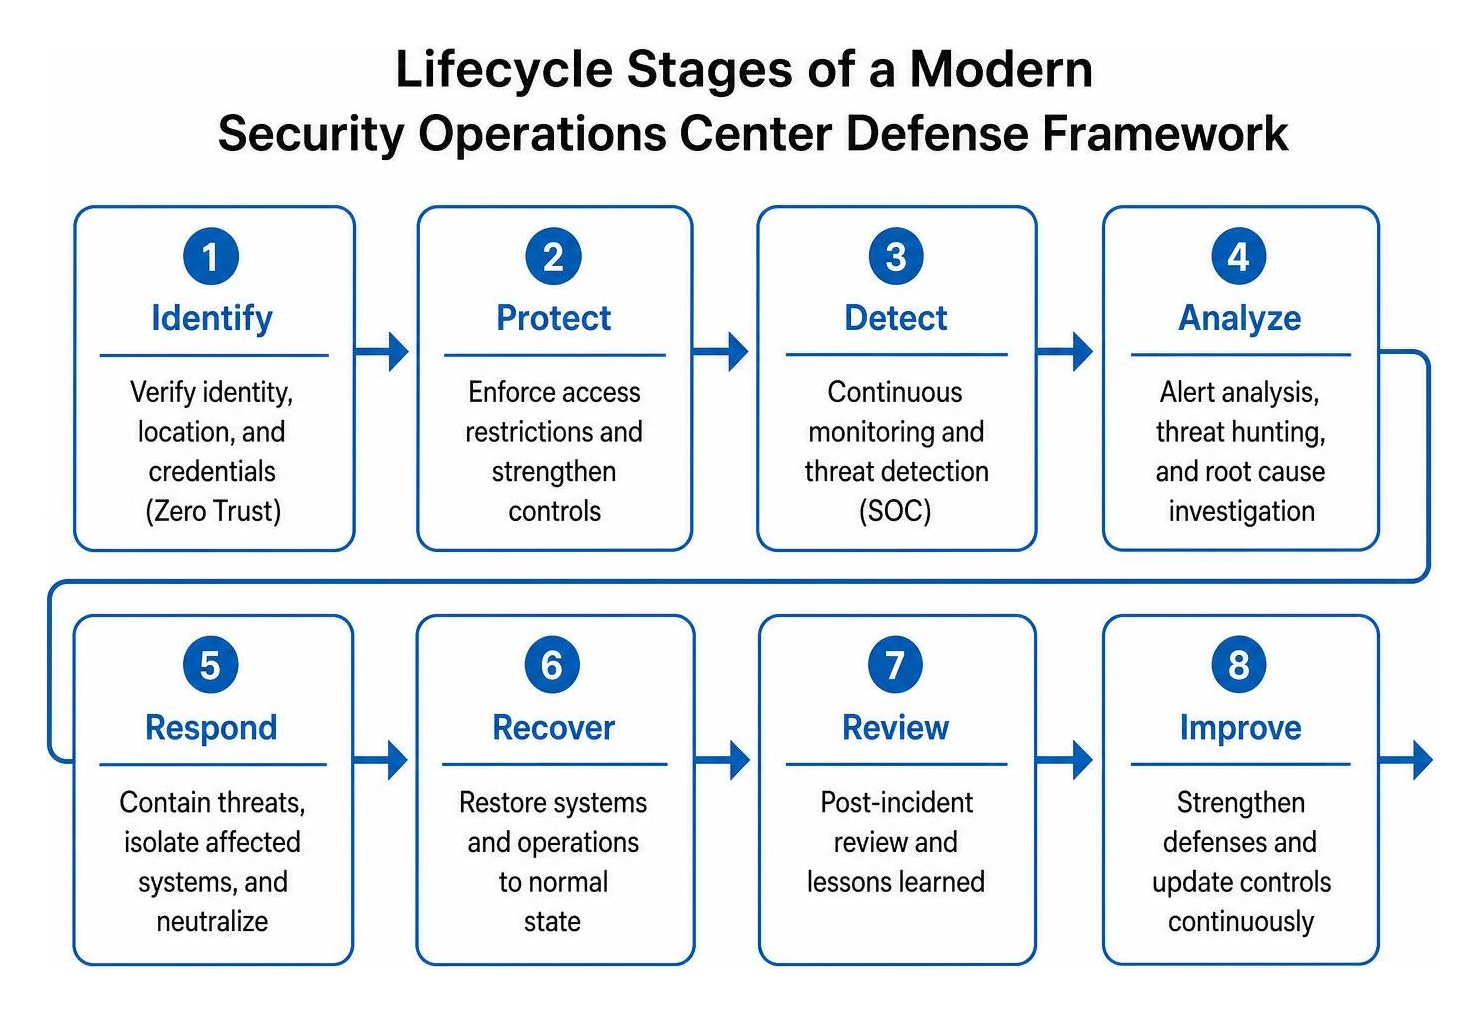
When I talk with facilities managers and business leaders across regions like Bethesda, MD, Richmond, VA, and Houston, TX, I often see how quickly security expectations have changed. The idea of a simple perimeter fence or basic network firewall is no longer sufficient. Modern threats require a shared responsibility model rooted in zero-trust architecture. This approach constantly verifies identity, location, and credentials before granting access to physical properties or sensitive digital data.
To get the full picture, it helps to understand the ins and outs of security companies and how different service models handle various elements of defense. Modern providers leverage multitenancy architecture to pool advanced platforms, making enterprise-grade defense accessible and budget-friendly for mid-sized organizations.
| Service Model | Primary Focus | Operational Hub | Key Capabilities | Typical Outcome |
|---|---|---|---|---|
| Managed Service Provider (MSP) | IT Infrastructure & System Uptime | Network Operations Center (NOC) | Patch management, cloud provisioning, user support | High availability and seamless workplace technology |
| Managed Security Service Provider (MSSP) | Enterprise Cyber Defense & Compliance | Security Operations Center (SOC) | Continuous log monitoring, vulnerability scanning, SIEM | Reduced attack surface and audit-ready governance |
| Managed Detection & Response (MDR) | Threat Hunting & Incident Response | Specialized Threat Operations Hub | Autonomous containment, root cause triage, endpoint isolation | Rapid containment of live cyber attacks |
MSSP vs MSP: Differentiating Cyber Defense from IT Infrastructure
One of the most frequent misconceptions I encounter is confusing an MSP with an MSSP. Think of it like this: an MSP is like a master mechanic who keeps your engine running smoothly, while an MSSP is the specialized vehicle armor and defensive system built to withstand active road hazards.
MSPs manage day-to-day IT systems. They monitor bandwidth, keep applications online, and run a Network Operations Center (NOC) dedicated to uptime and convenience. In contrast, an MSSP operates a Security Operations Center (SOC). Their mission is access restriction, threat neutralization, and vulnerability containment. While an MSP prioritizes availability, an MSSP prioritizes defense.
Core Categories of Managed Security Service Providers
Not all security partners offer the exact same scope of work. I generally organize external security providers into three core functional categories:
- Consultancy and Advisory Services: These firms provide high-level leadership through virtual Chief Information Security Officer (vCISO) models, security risk management frameworks, and readiness assessments. They bridge the gap between technical operations and executive boardrooms.
- Security Operations (Core Monitoring): Providers in this space deliver round-the-clock event monitoring, continuous alert analysis, and rapid triage across enterprise environments.
- Technology Maintenance and Management: These partners handle the heavy lifting of security infrastructure. They configure firewalls, manage Privileged Access Management (PAM) platforms, and keep detection rule sets updated.
Many growing companies thrive under a co-managed security model. This approach pairs internal IT personnel with an external partner to share tasks and eliminate single points of operational failure.
Managed Security Services vs Dedicated MDR Solutions
While an MSSP offers a broad security umbrella covering governance and tool maintenance, Managed Detection and Response (MDR) delivers deep, specialized threat hunting. MDR providers focus on Endpoint Detection and Response (EDR) and Extended Detection and Response (XDR) telemetry.
When suspicious behavior appears on a server or workstation, MDR analysts step in to contain the issue, isolate affected machines, and eliminate the threat before it spreads. Utilizing specialized MDR services alongside a broader security foundation creates a layered strategy against complex intrusions.
Essential Capabilities and Services for Full-Spectrum Defense
A comprehensive defense strategy connects disparate platforms into a clear, unified picture. Leading operations align detection rules with established standards, such as the MITRE ATT&CK framework, ensuring every alert corresponds to a known attacker tactic or technique.
24/7 Security Operations Center Monitoring and Incident Response
Security threats do not follow standard business hours. High-availability SOC facilities offer round-the-clock coverage, ensuring critical events receive human review within minutes. Tier-one analysts filter baseline noise, while senior engineers handle direct incident mitigation. This human expertise ensures true threats receive immediate containment while preventing operational disruptions from routine false alarms.
Vulnerability Scanning and Attack Surface Exposure Management
Keeping ahead of threats requires continuous exposure management. I encourage organizations to look beyond basic internal scans and evaluate their entire digital footprint. Modern security risk management includes:
- Scanning peripheral and third-party systems that connect to your core network.
- Enforcing Privileged Access Management (PAM) policies to limit administrative access.
- Monitoring external digital footprints to defend against brand impersonation and executive phishing schemes.
Regulatory Compliance and Audit-Ready Governance Support
Navigating regulatory requirements can quickly overwhelm an internal team. Modern providers automate log collection and evidence mapping for frameworks like GDPR, HIPAA, PCI DSS, and SOC 2 Type II. This continuous data collection turns annual audit preparation into a manageable, routine process. If you operate in the Mid-Atlantic, working with a provider familiar with regional business requirements can help align digital compliance needs with local standards.
Strategic Benefits and Operational Challenges in Managed Defense
Partnering with an external security firm offers clear strategic benefits, such as predictable subscription costs and expanded expertise. Understanding how private security services can safeguard your assets helps organizations support property value, personnel, and daily operations.
Cost Efficiencies, Tool Consolidation, and Talent Gap Resolution
The modern security landscape faces a major obstacle: tool sprawl. The average enterprise maintains over 50 separate security tools, creating integration challenges and coverage blind spots. Consolidating under a single, experienced partner simplifies software overhead and streamlines vendor communications.
Finding, hiring, and retaining qualified security analysts remains expensive and time-consuming. Partnering with an external provider gives you immediate access to a complete team of specialists at a fraction of the cost of building an in-house 24/7 operations center.
Navigating AI-Driven Threats and Alert Fatigue
With AI-driven attacks rising by 56%, automated defense mechanisms have become essential. Modern security architectures use machine learning to filter out everyday noise, resolving routine notifications automatically so human analysts can focus their attention on complex, high-priority issues.
How to Evaluate and Vet Your Security Partner
Selecting a dependable partner requires looking beyond glossy sales presentations. Reviewing a reliable guide to private security agencies will help you ask the right questions and ensure the firm’s capabilities align with your facility and corporate requirements.
Use this checklist during vendor evaluations:
- Does the provider hold third-party credentials like SOC 2 Type II certifications?
- Do they carry adequate Cyber Insurance and Errors & Omissions coverage?
- Are escalation procedures clearly documented in a RACI matrix?
- Do their monitoring platforms integrate smoothly with your ticketing systems (e.g., ServiceNow, Jira)?
- Can they scale operations dynamically during seasonal peaks or unexpected incidents?
Key Criteria for Evaluating Security Service Providers
Sector experience matters. Managing a healthcare campus in Boston, MA requires different protocols than securing a logistics hub in Dallas, TX or a corporate headquarters in Miami, FL. Look for partners that thoroughly vet and train their staff. To understand how rigorous standards create better outcomes, read this definitive guide to security training services.
SLAs, Integration Capabilities, and Multi-Layered Defense
Service Level Agreements (SLAs) must include clear, measurable performance goals. Key metrics include:
- Mean Time to Detect (MTTD): How quickly a suspicious event is identified.
- Mean Time to Respond (MTTR): The time required to triage and contain a validated incident.
Effective security also bridges digital defenses and physical safety. Unified operations combine on-site access management with active digital surveillance, creating total situational awareness across your properties. For advanced operational requirements, recognized resources such as the NIST Cybersecurity Framework can help organizations evaluate multi-layered operational readiness.
Frequently Asked Questions About Managed Security Operations
What is the primary difference between an MSP and an MSSP?
An MSP focuses on general IT administration, equipment uptime, and software deployment through a Network Operations Center (NOC). An MSSP focuses specifically on defense, threat mitigation, vulnerability management, and continuous monitoring through a Security Operations Center (SOC).
How do security providers assist with regulatory compliance audits?
Security partners deploy automated tools that continuously log network events and maintain audit-ready records. They map security controls directly to frameworks such as HIPAA, PCI DSS, and SOC 2, providing validated evidence to external auditors and minimizing preparation strain on internal teams.
Why are organizations combining cyber defense with physical security solutions?
Modern security risks are interconnected. An unauthorized person using a lost physical access badge can compromise a server room just as easily as an external hacker exploits a network vulnerability. Combining physical access control, trained personnel, and digital monitoring ensures total defense across every operational layer.
Conclusion
Building an effective security foundation requires an integrated approach to security risk management, clear accountability, and reliable partners. Whether maintaining smooth operations across commercial facilities or establishing defensive layers across digital infrastructure, proactive preparation is essential for long-term business resilience.
At Admiral Security, I take pride in delivering dependable, responsive solutions built on authenticity, logic, and empathy. Our footprint spans major business centers across Maryland, Delaware, Virginia, North Carolina, Florida, Texas, and Massachusetts. Discover how our dedicated teams and advanced integration can support your properties by exploring our comprehensive security solutions and the Admiral Advantage today.